About Bundle
The IAM–PAM Membership Self-Learning Program is a comprehensive learning package designed for IT professionals, cybersecurity learners, IAM engineers, administrators, and beginners who want to develop practical skills across Identity & Access Management (IAM), Identity Governance & Administration (IGA), and Privileged Access Management (PAM).
The program provides access to multiple identity-security technology courses in one learning path, helping learners understand how modern organizations manage identities, authentication, authorization, user lifecycle, access governance, provisioning, privileged accounts, SSO, MFA, and enterprise application access. These are core areas of modern IAM practice.
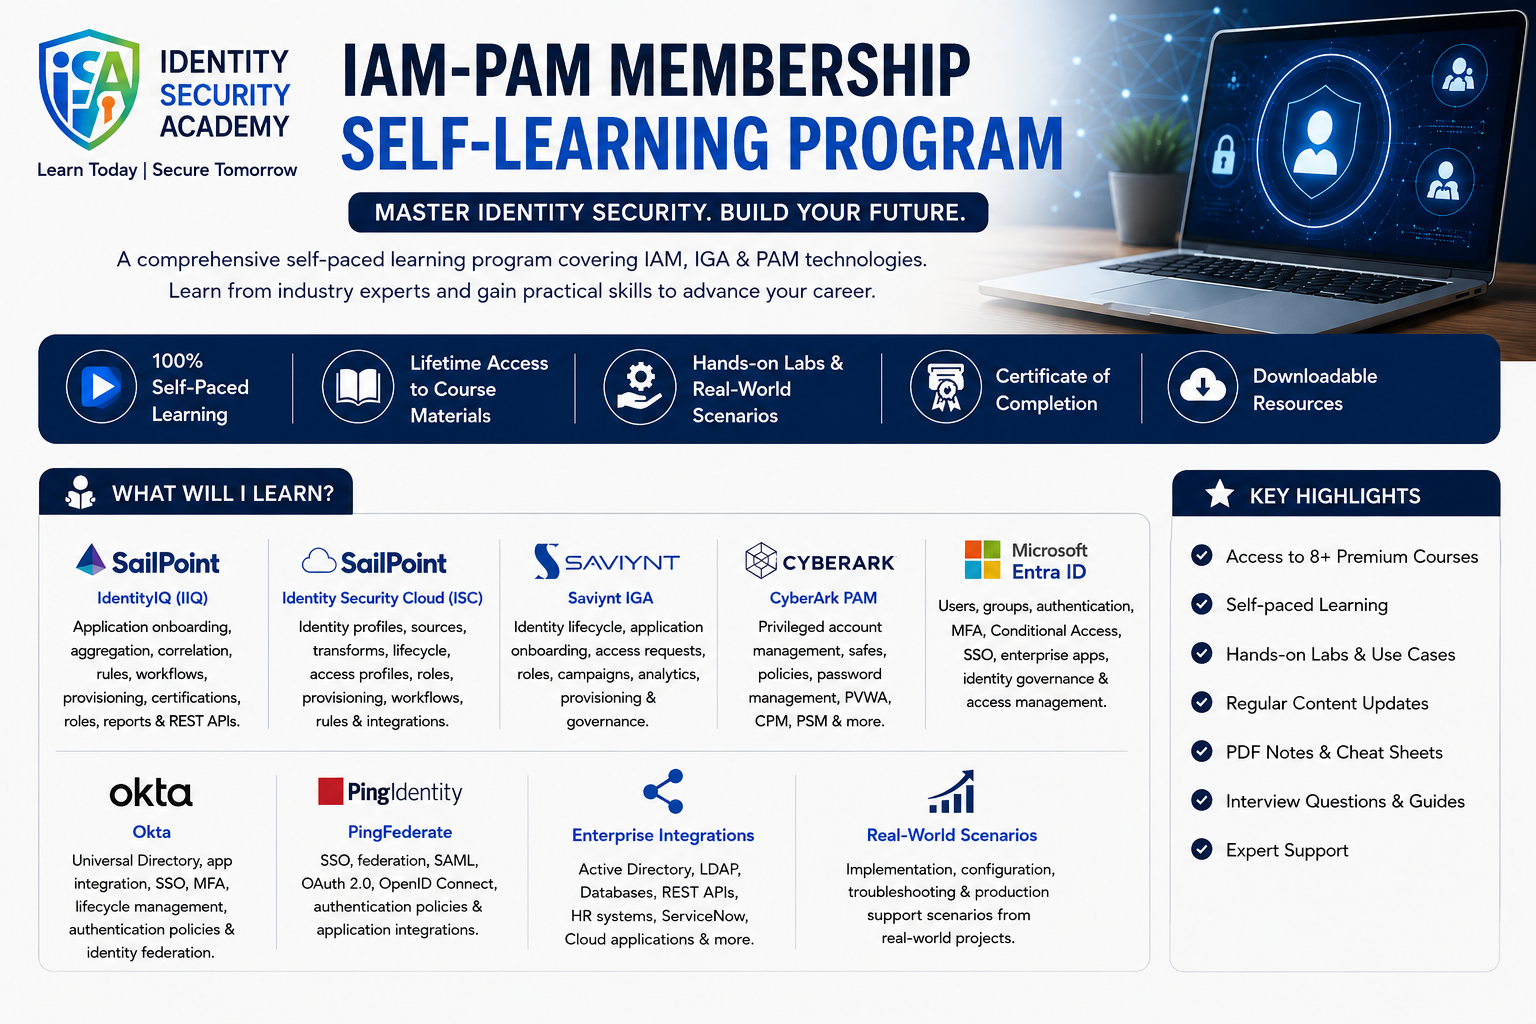
Learners can develop skills across leading identity-security platforms, including:
- SailPoint IdentityIQ (IIQ) – Identity Governance & Administration
- SailPoint Identity Security Cloud (ISC) – Cloud Identity Security
- Saviynt IGA – Identity Governance & Administration
- CyberArk PAM – Privileged Access Management
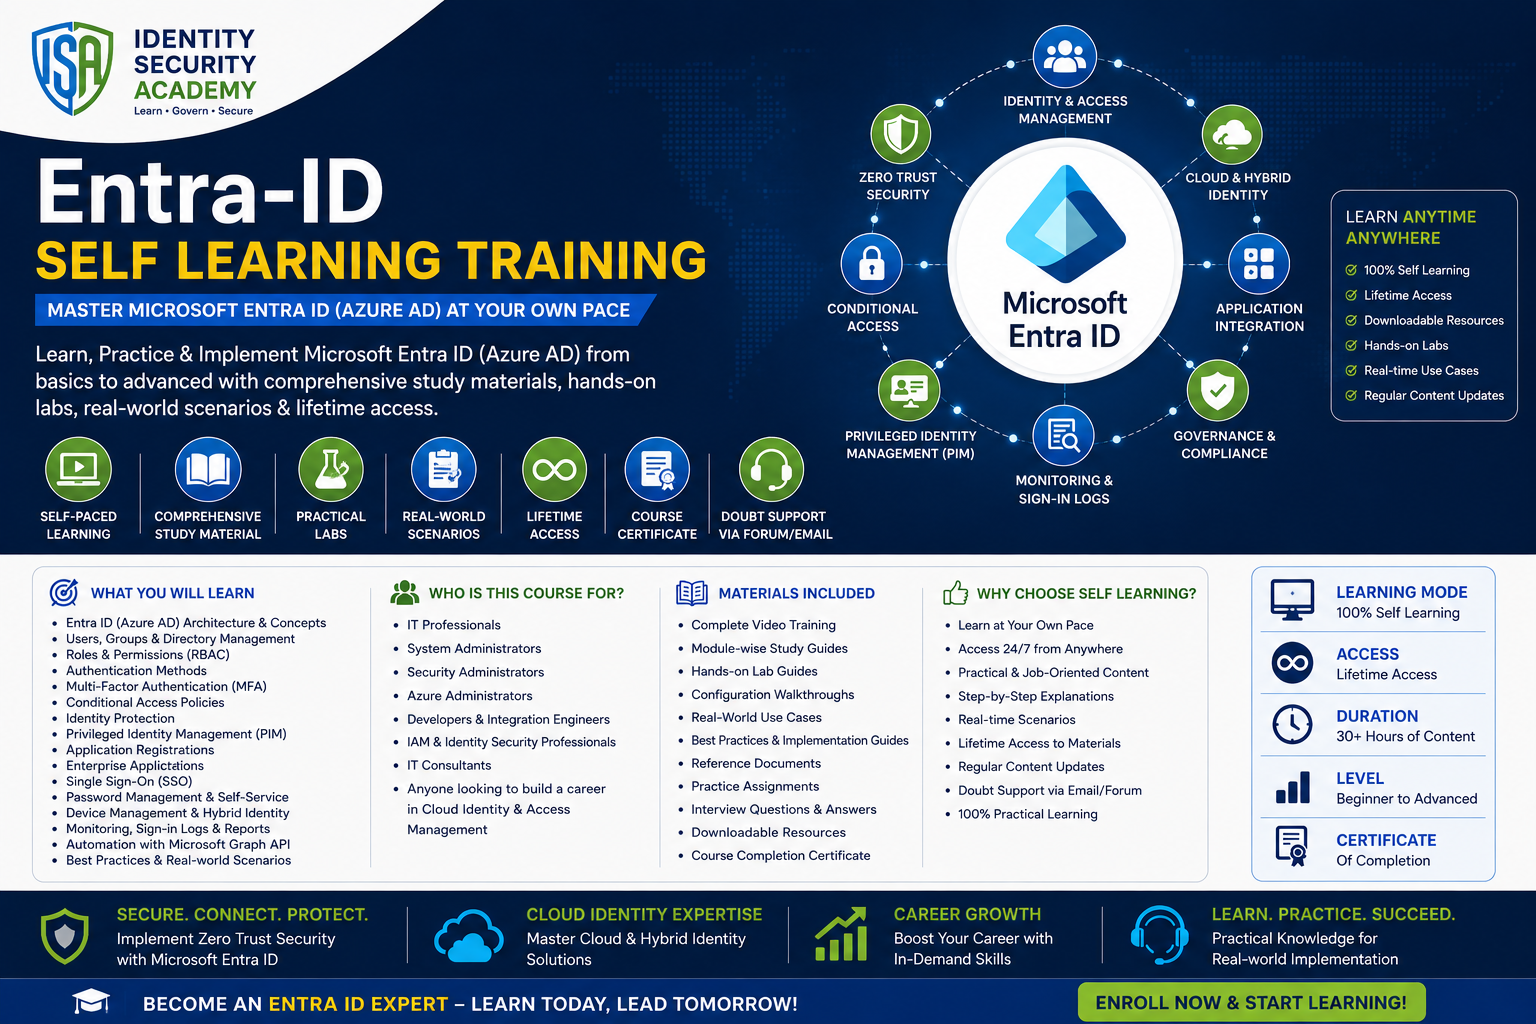
- Microsoft Entra ID – Cloud Identity & Access Management
- Okta – IAM, SSO & Authentication
- PingFederate – Federation, SSO & Authentication
The program follows a self-paced learning model, allowing learners to study according to their own schedule and revisit training materials whenever needed during their membership period. The focus is not only on theoretical concepts but also on practical configurations, implementation scenarios, troubleshooting approaches, and real-world IAM/PAM use cases.
It is suitable for professionals looking to upskill in Identity Security, move into IAM/IGA/PAM roles, strengthen implementation knowledge, or prepare for technical interviews and project responsibilities.
Program Focus: Learn → Practice → Implement → Build Real-World Identity Security Skills.
Courses in the Bundle (7)
-

SailPoint-IIQ-Developer-SelfLeaning
By Admin | Category: Development, IAM
-

Saviynt-IGA-Develper-SelfLearning
By Admin | Category: Development, IAM
-

SailPoint-Identity-Security-Cloud-SelfLearning
By Admin | Category: Development
-
Ping-Federate-SelfLearning-Program
By Admin | Category: Development, IAM
-
-

-